Services
Managed Security Operations
Monitoring, triage, and patching run as an ongoing service, so detection and remediation do not depend on who is on shift.
Book an assessment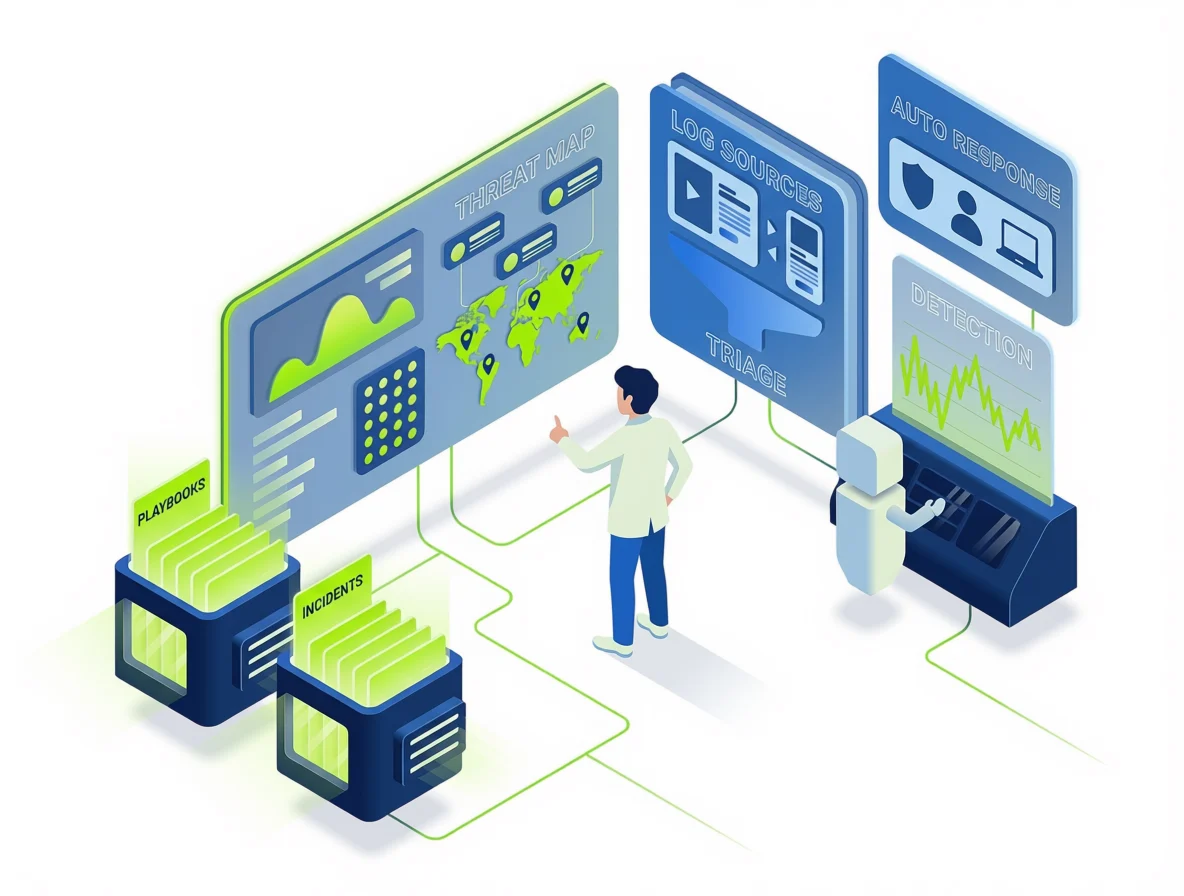
What this covers
Log sources, coverage hours and escalation paths are agreed before onboarding. What runs day to day below follows that agreement rather than the judgement of whoever is on shift.
-
Log analysis and correlation
Events correlated across sources so related signals surface as one incident rather than several disconnected alerts.
-
Threat intelligence integration
External intelligence feeds matched against your environment, filtered down to what is actually relevant to your stack.
-
Incident severity classification
A consistent severity model, so escalation is driven by defined criteria rather than by whoever picks up the alert.
-
Incident documentation and analysis
Written post-incident analysis covering what happened, what was affected, and what changes prevent a repeat.
-
Continuous vulnerability monitoring
Ongoing tracking of exposure across your estate, tied to the patch pipeline rather than reported in isolation.
-
Customised patching strategies
Patch scheduling built around your maintenance windows and uptime commitments, not a fixed vendor calendar.
-
Emergency patching and rollback
Out-of-band response for actively exploited vulnerabilities, with a tested rollback path before anything is deployed.
-
Incident response plan assessment
Tabletop exercises that test the plan you have, and identify the steps that fail under time pressure.
Included offerings
These run as continuing services rather than one-off engagements, so scope is set by what you need covered, at what hours, and who acts on the output.
Where this applies
All sectorsOther practices
Let's talk
Start your security journey with us
Tell us what you need tested and our engineers will guide you to the right engagement.
Book an assessment