
Recently, the data extortion gang Lapsus$ published a massive collection of confidential data, claiming to be from Samsung Electronics, the South Korean consumer electronics behemoth.
Lapsus$ released a 20GB document collection from 1TB of data taken from Nvidia GPU designer less than a week ago.
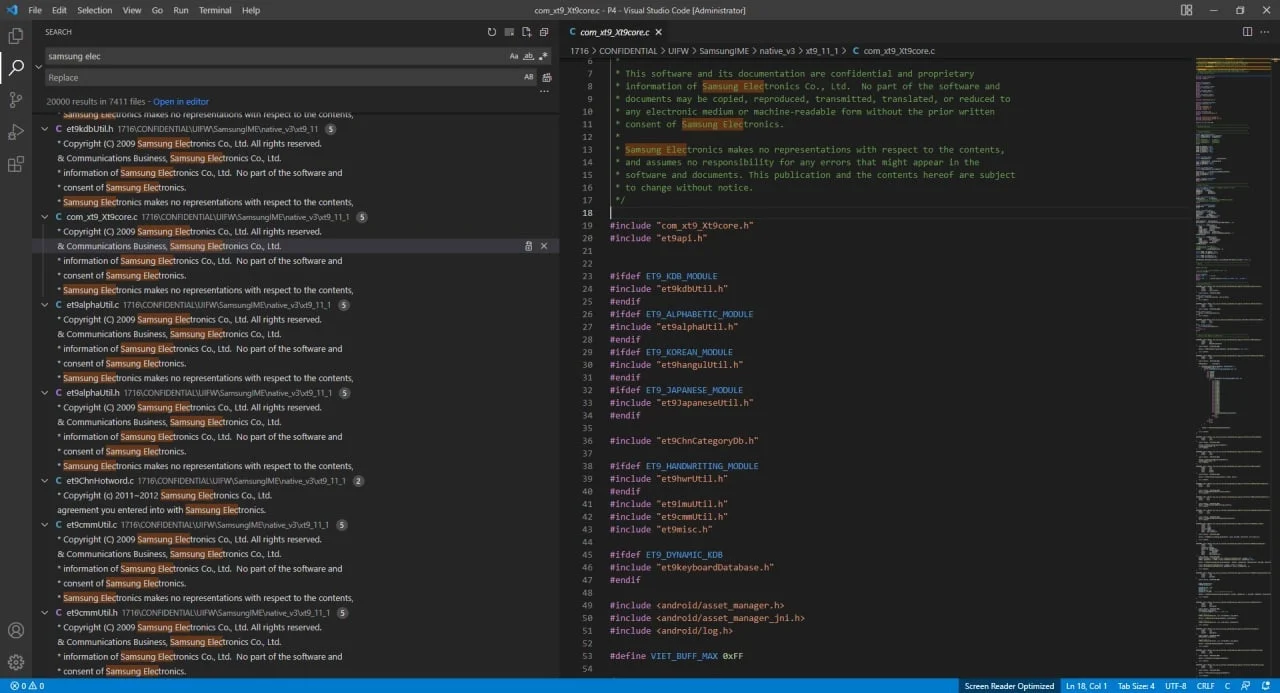
The extortion gang teased about revealing Samsung data with a snapshot of C/C++ instructions in Samsung software in a previous note.
Lapsus$ issued a summary of the imminent leak shortly after tantalizing their followers, claiming that it contained "secret Samsung source code" stemming from a breach.
Source code for every Trusted Applet (TA) installed in Samsung’s TrustZone environment used for sensitive operations (e.g. hardware cryptography, binary encryption, access control)
Algorithms for all biometric unlock operations
Bootloader source code for all recent Samsung devices
Confidential source code from Qualcomm
Source code for Samsung’s activation servers
Full source code for technology used for authorizing and authenticating Samsung accounts, including APIs and services
If the information above is correct, Samsung has had a big data breach that could result in significant financial loss.
Lapsus$ divided the disclosed data into three compressed files totaling about 190GB and uploaded them to a torrent that appears to be very popular, with over 400 peers spreading the content. The extortion organization further stated that it would boost the download speed by deploying more servers.
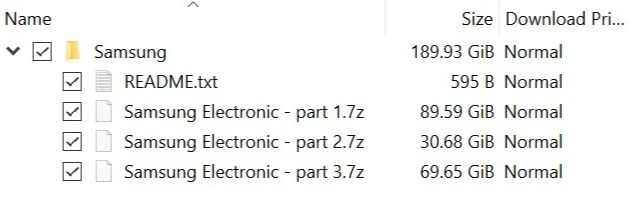
A brief explanation of the content contained in each of the three vaults is also included in the torrent:
Part 1 contains a source code dump as well as other information about Security/Defense/Knox/Bootloader/TrustedApps and other topics.
Part 2 includes a source code dump as well as info on device security and encryption.
Samsung GitHub repositories for mobile defensive engineering, Samsung account backend, Samsung pass backend/frontend, and SES are all included in Part 3. (Bixby, Smartthings, store)
It's unknown if Lapsus$ attempted to contact Samsung for a ransom, like they did with Nvidia.
For more information visit us on: www.nexixsecuritylabs.com
To schedule an audit you can contact us at: contact@nexixsecuritylabs.com
Your Security | Our Concern